

Summary
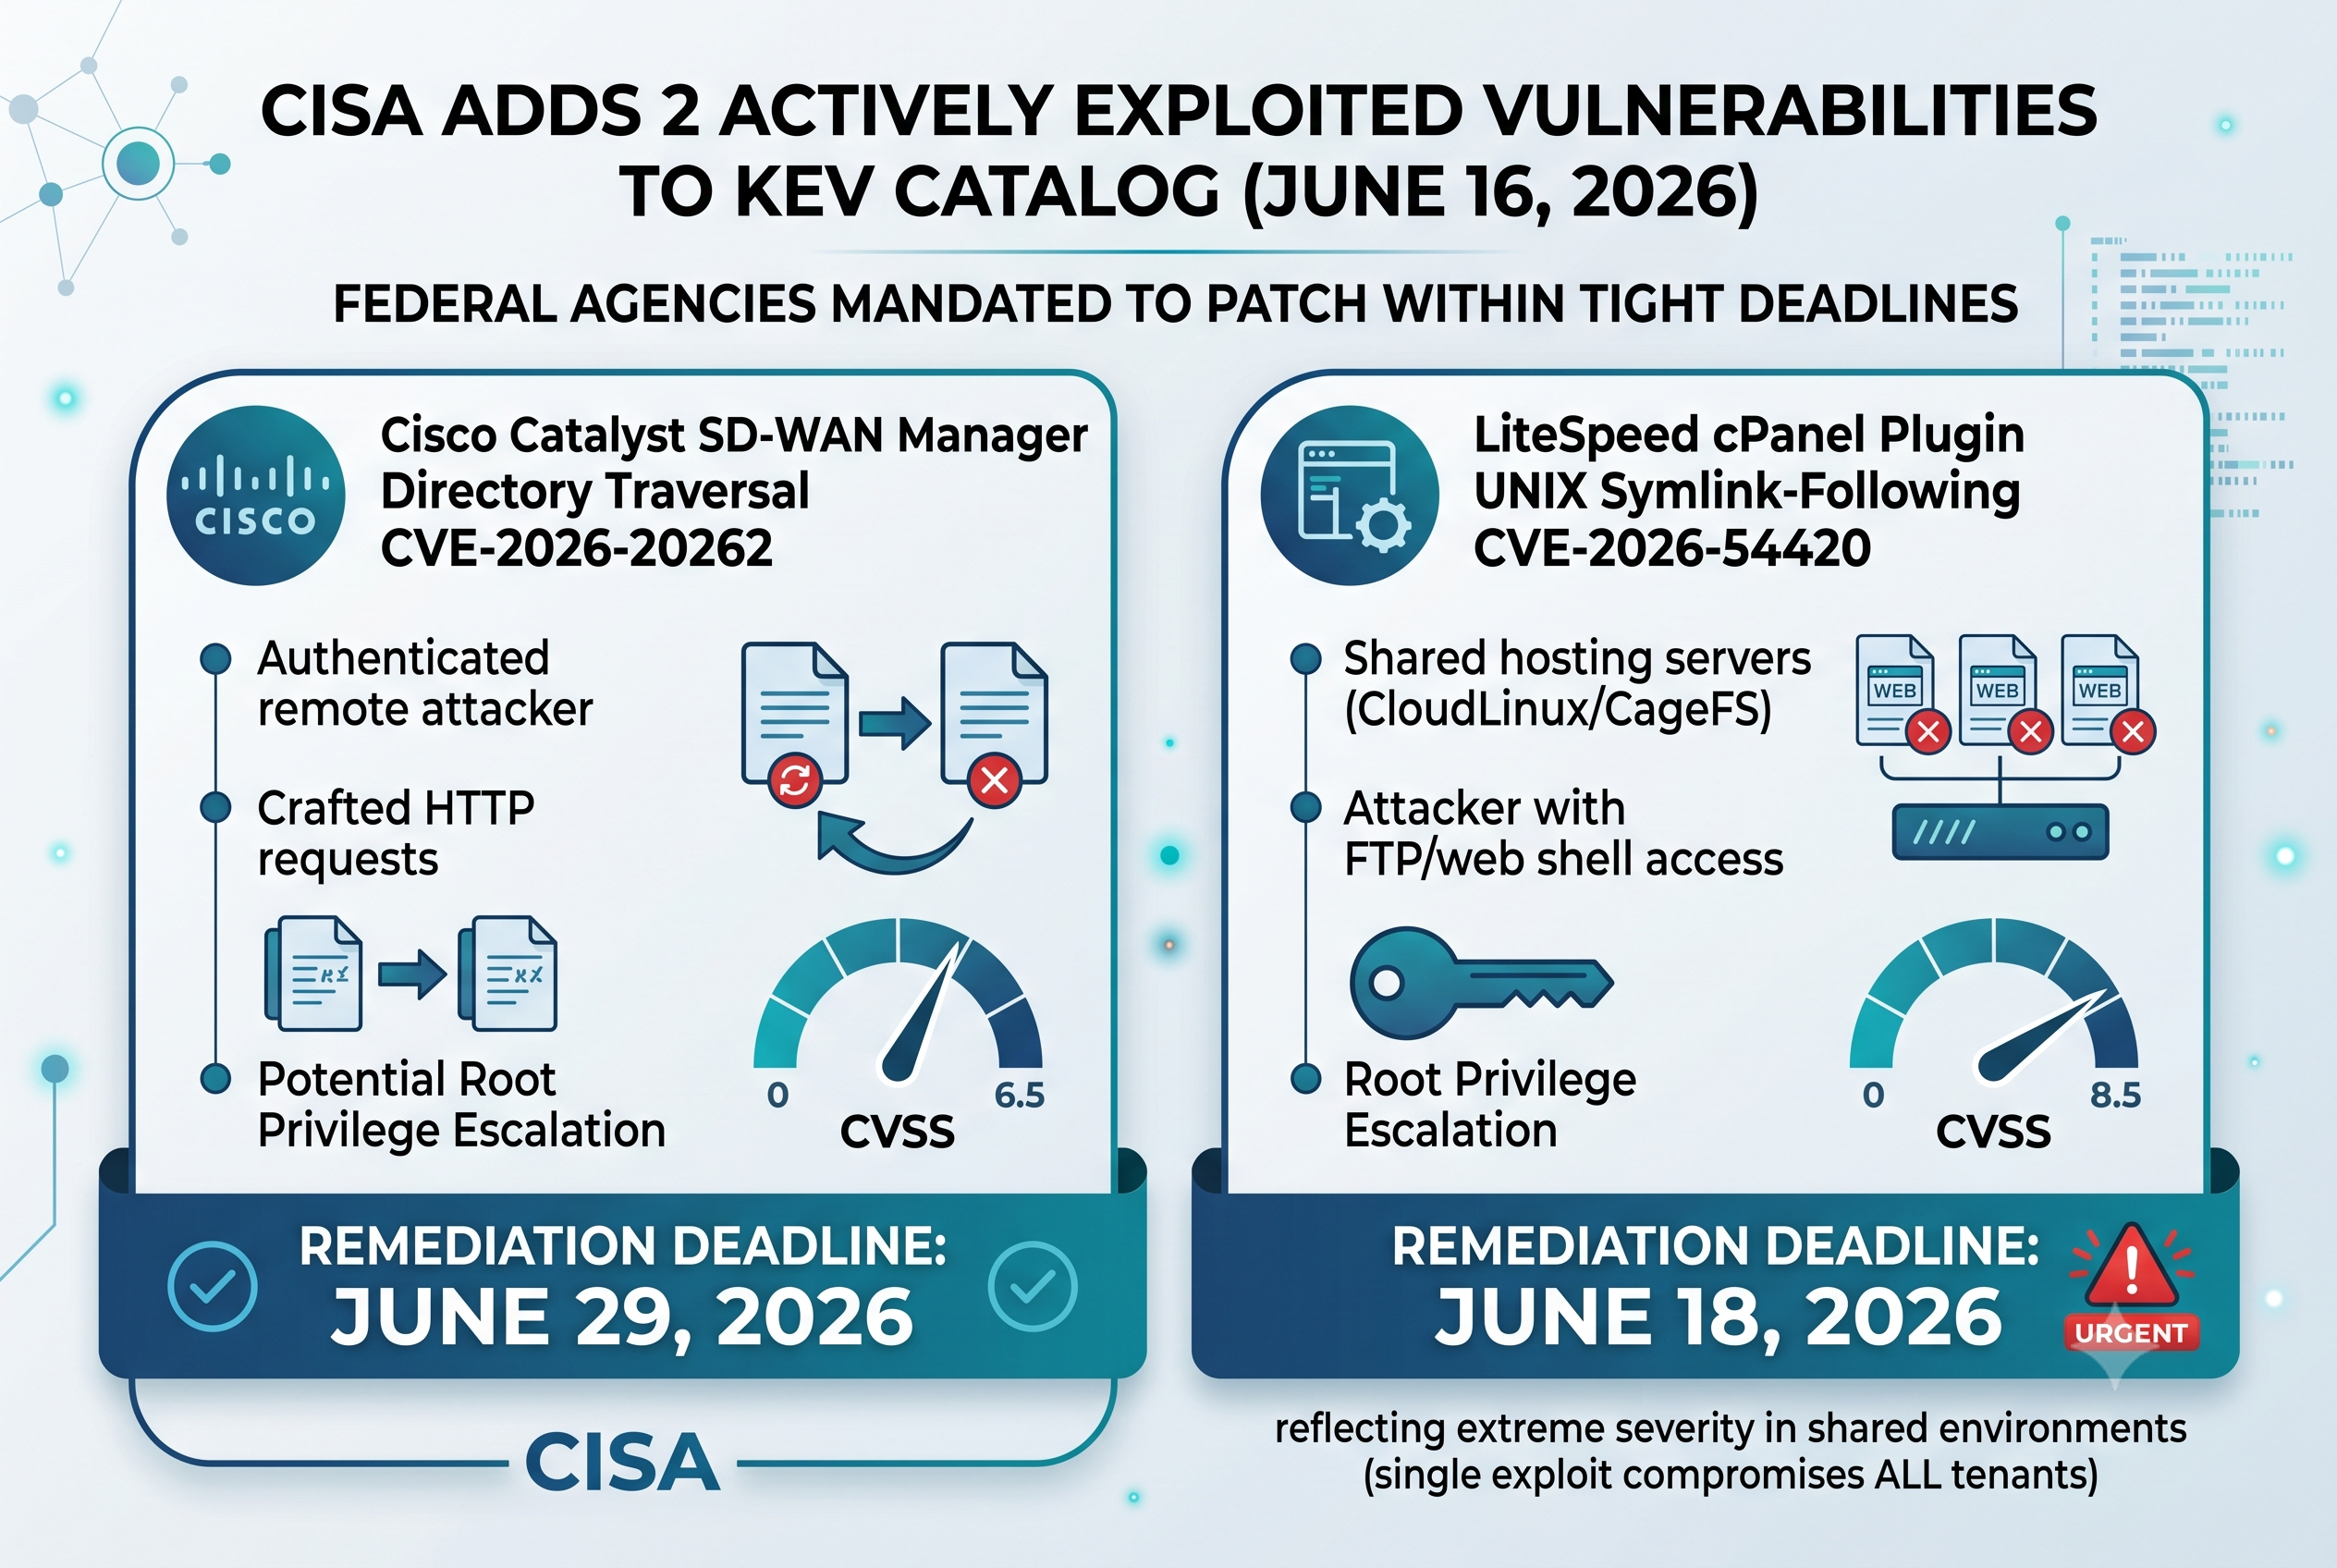
On June 16, 2026, the Cybersecurity and Infrastructure Security Agency (CISA) added two actively exploited vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, mandating federal agencies to patch within tight deadlines.
The first, CVE-2026-20262, is a directory traversal vulnerability in Cisco Catalyst SD-WAN Manager (CVSS 6.5) that allows an authenticated remote attacker to create or overwrite files on the underlying operating system via crafted HTTP requests, potentially escalating privileges to root. Federal agencies must remediate by June 29, 2026.
The second, CVE-2026-54420, is a UNIX symlink-following vulnerability in the LiteSpeed cPanel Plugin (CVSS 8.5). The flaw enables attackers with FTP or web shell access on shared hosting servers running CloudLinux or CageFS to escalate privileges to root. CISA has set an aggressive remediation deadline of June 18, 2026 — just two days out — reflecting confirmed active exploitation and the severity of impact on shared hosting environments where a single privilege escalation can compromise every tenant on the server.
Source
CISA Alert — Two New KEV Entries · The Hacker News · Security Affairs
Commentary
The LiteSpeed cPanel Plugin vulnerability is particularly concerning in context: combined with the ongoing mass exploitation of CVE-2026-41940 (the cPanel/WHM authentication bypass), shared hosting environments are under simultaneous pressure from multiple critical attack vectors. Hosting providers running cPanel with LiteSpeed and CloudLinux — an extremely common stack — need to treat both CVEs as a combined emergency.
The Cisco SD-WAN Manager flaw is more targeted but equally insidious. Directory traversal to root in network management infrastructure gives an attacker the keys to an organization’s entire WAN fabric. Defenders should cross-reference the KEV catalog regularly and treat CISA deadlines as maximums, not targets — patch now, not by the deadline.