

Summary
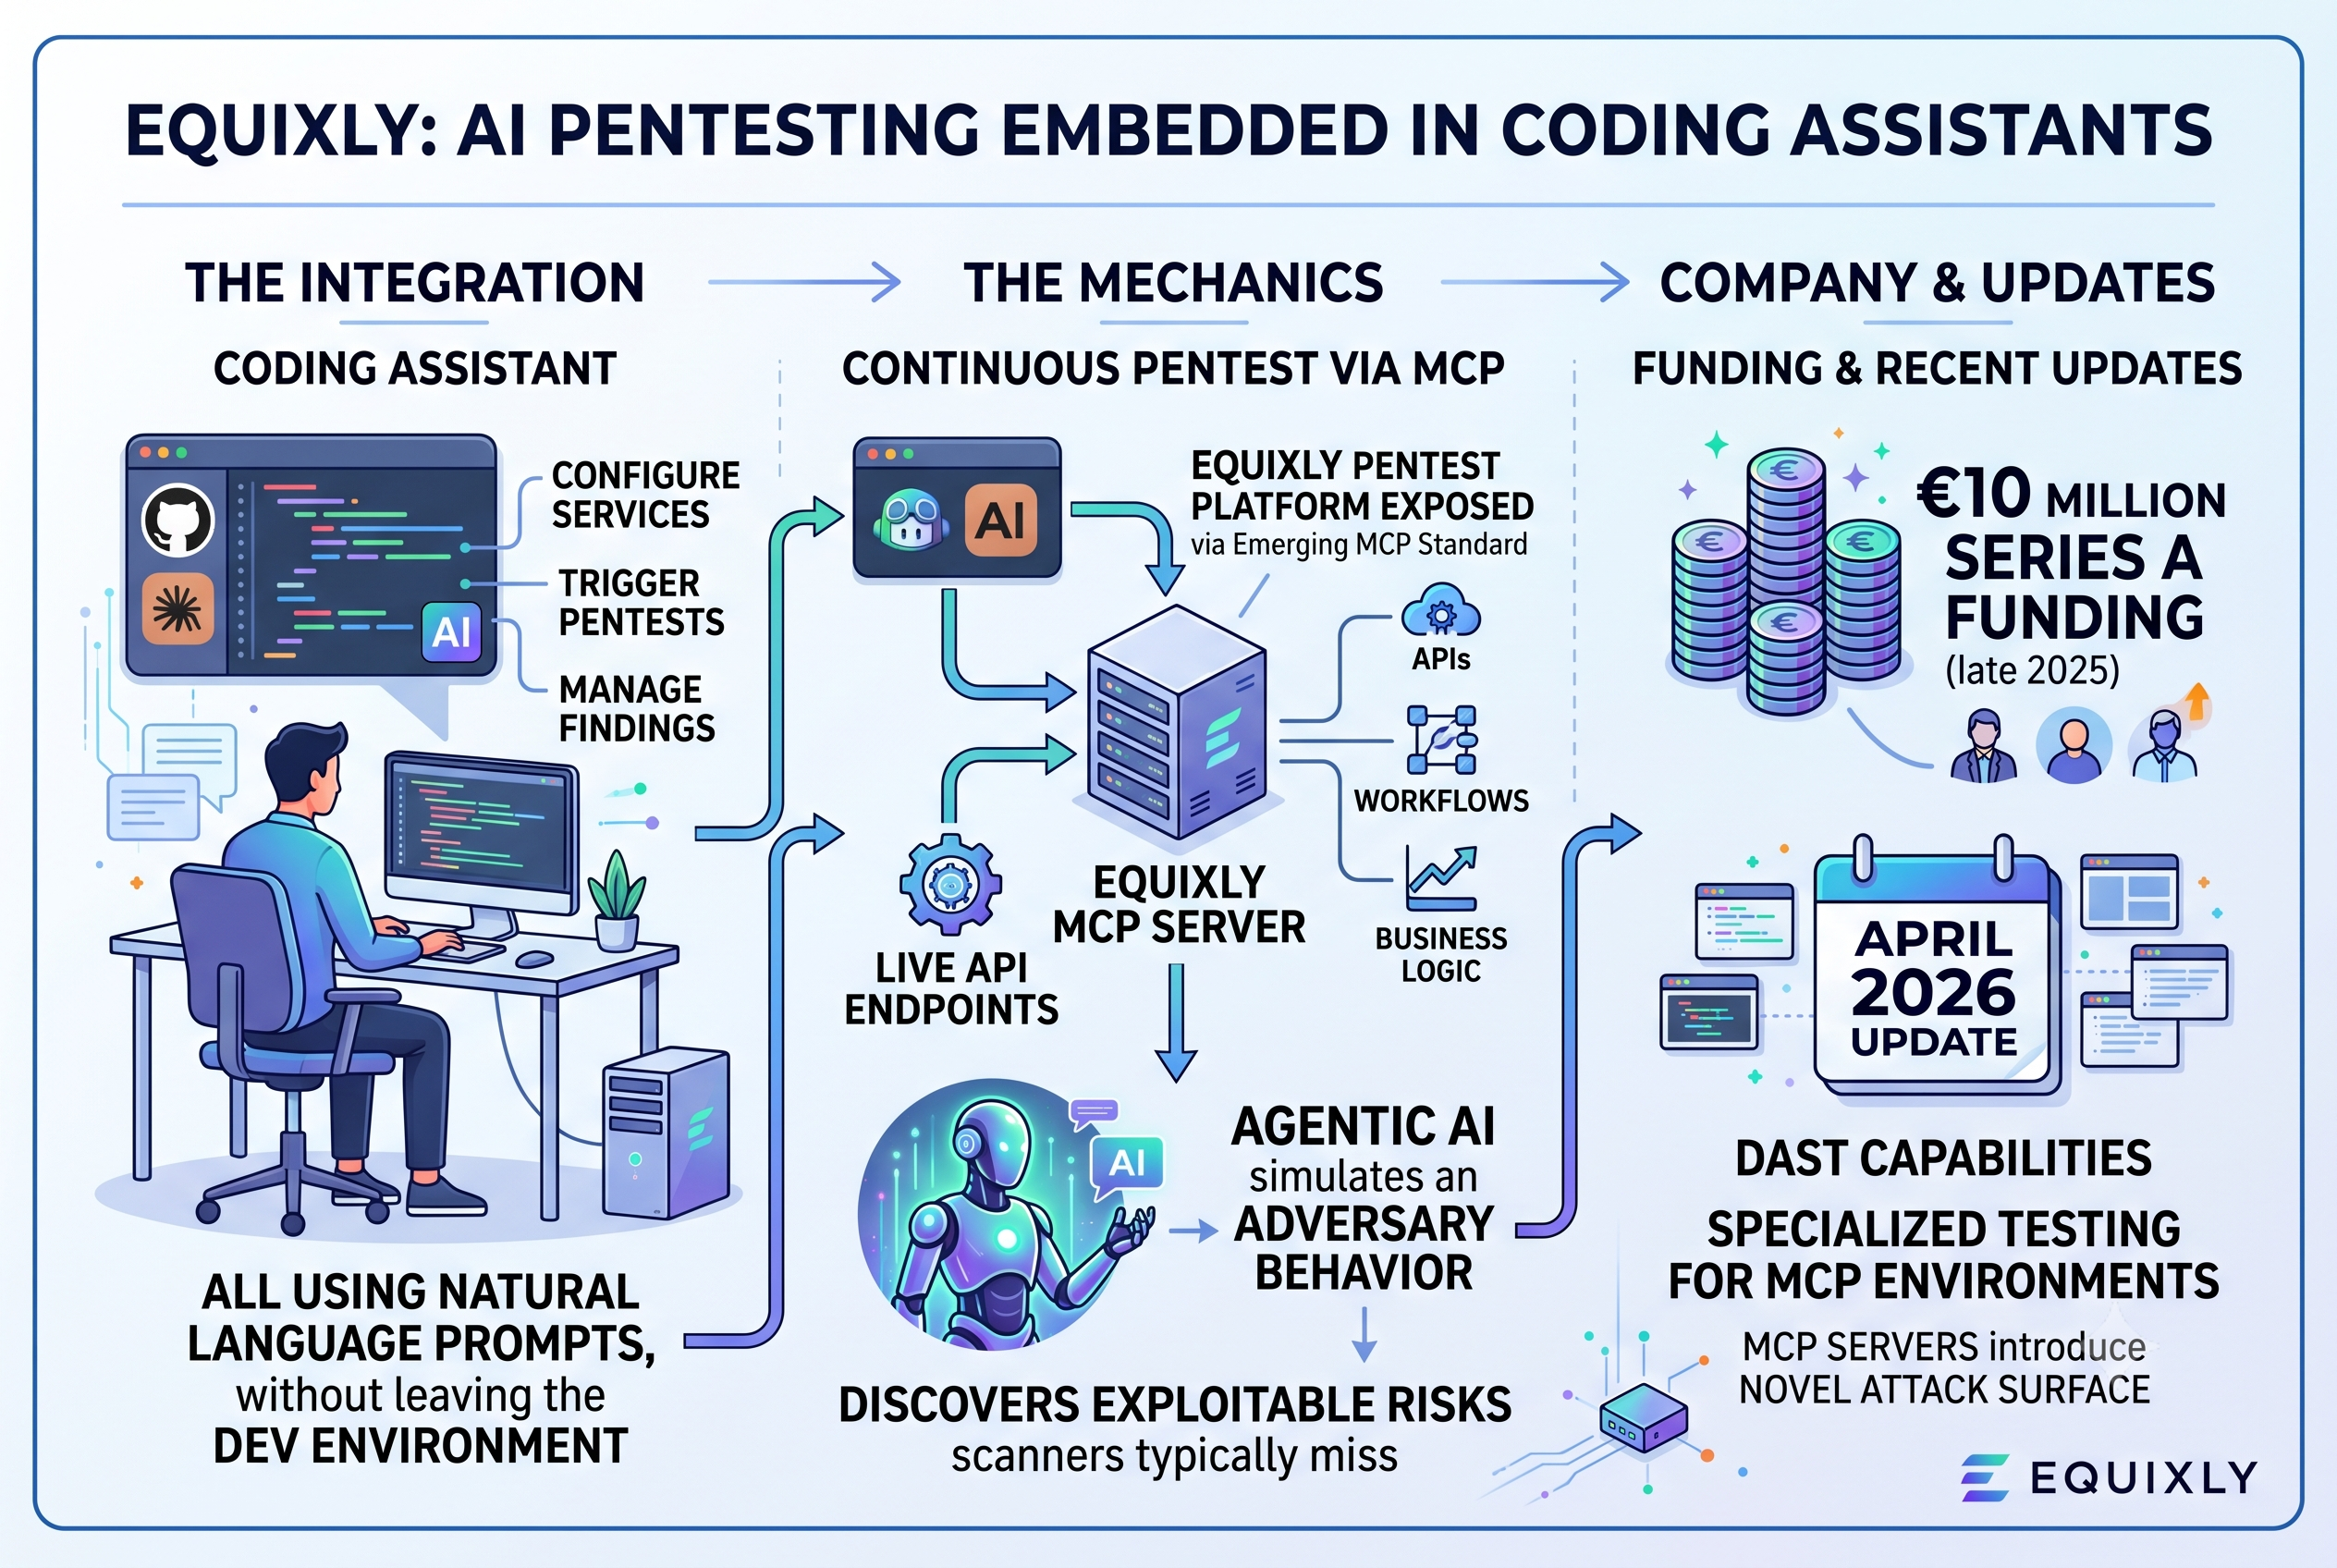
Equixly, an AI-powered offensive security platform, has launched a Model Context Protocol (MCP) integration that embeds continuous penetration testing capabilities directly into AI coding assistants like GitHub Copilot and Claude. Developers can now configure services, trigger pentests against live endpoints, and manage security findings using natural language prompts — all without leaving their development environment.
The integration exposes Equixly’s full continuous pentest platform via MCP, the emerging standard for connecting AI assistants to external systems. Developers add Equixly as an MCP server and interact with it through their existing AI coding workflow. The platform’s agentic AI simulates real adversary behavior to discover exploitable risks across APIs, workflows, and business logic that traditional scanners typically miss.
The announcement, made on June 15, follows Equixly’s €10 million Series A funding in late 2025 and an April 2026 product update that added DAST capabilities and specialized testing for MCP environments themselves — acknowledging that MCP servers introduce their own novel attack surface.
Source
Equixly — MCP Integration Launch
Commentary
This is a natural evolution of the shift-left security movement taken to its logical conclusion: instead of security being a gate that developers hit after writing code, the pentest lives inside the same AI assistant that helped write the code in the first place. The friction reduction is significant — developers who would never voluntarily open a separate security tool might actually run a pentest if it takes a single natural language prompt in their existing workflow.
The more interesting implication is for red teams: if continuous automated pentesting becomes a standard part of the dev loop, the baseline security posture of applications should rise, pushing red teamers toward more complex attack chains and business logic flaws that automated tools still struggle with. It is also worth noting the recursive nature of the problem — Equixly is testing MCP environments for security issues while simultaneously being delivered via MCP. The attack surface of AI tooling infrastructure remains an open frontier.