

Summary
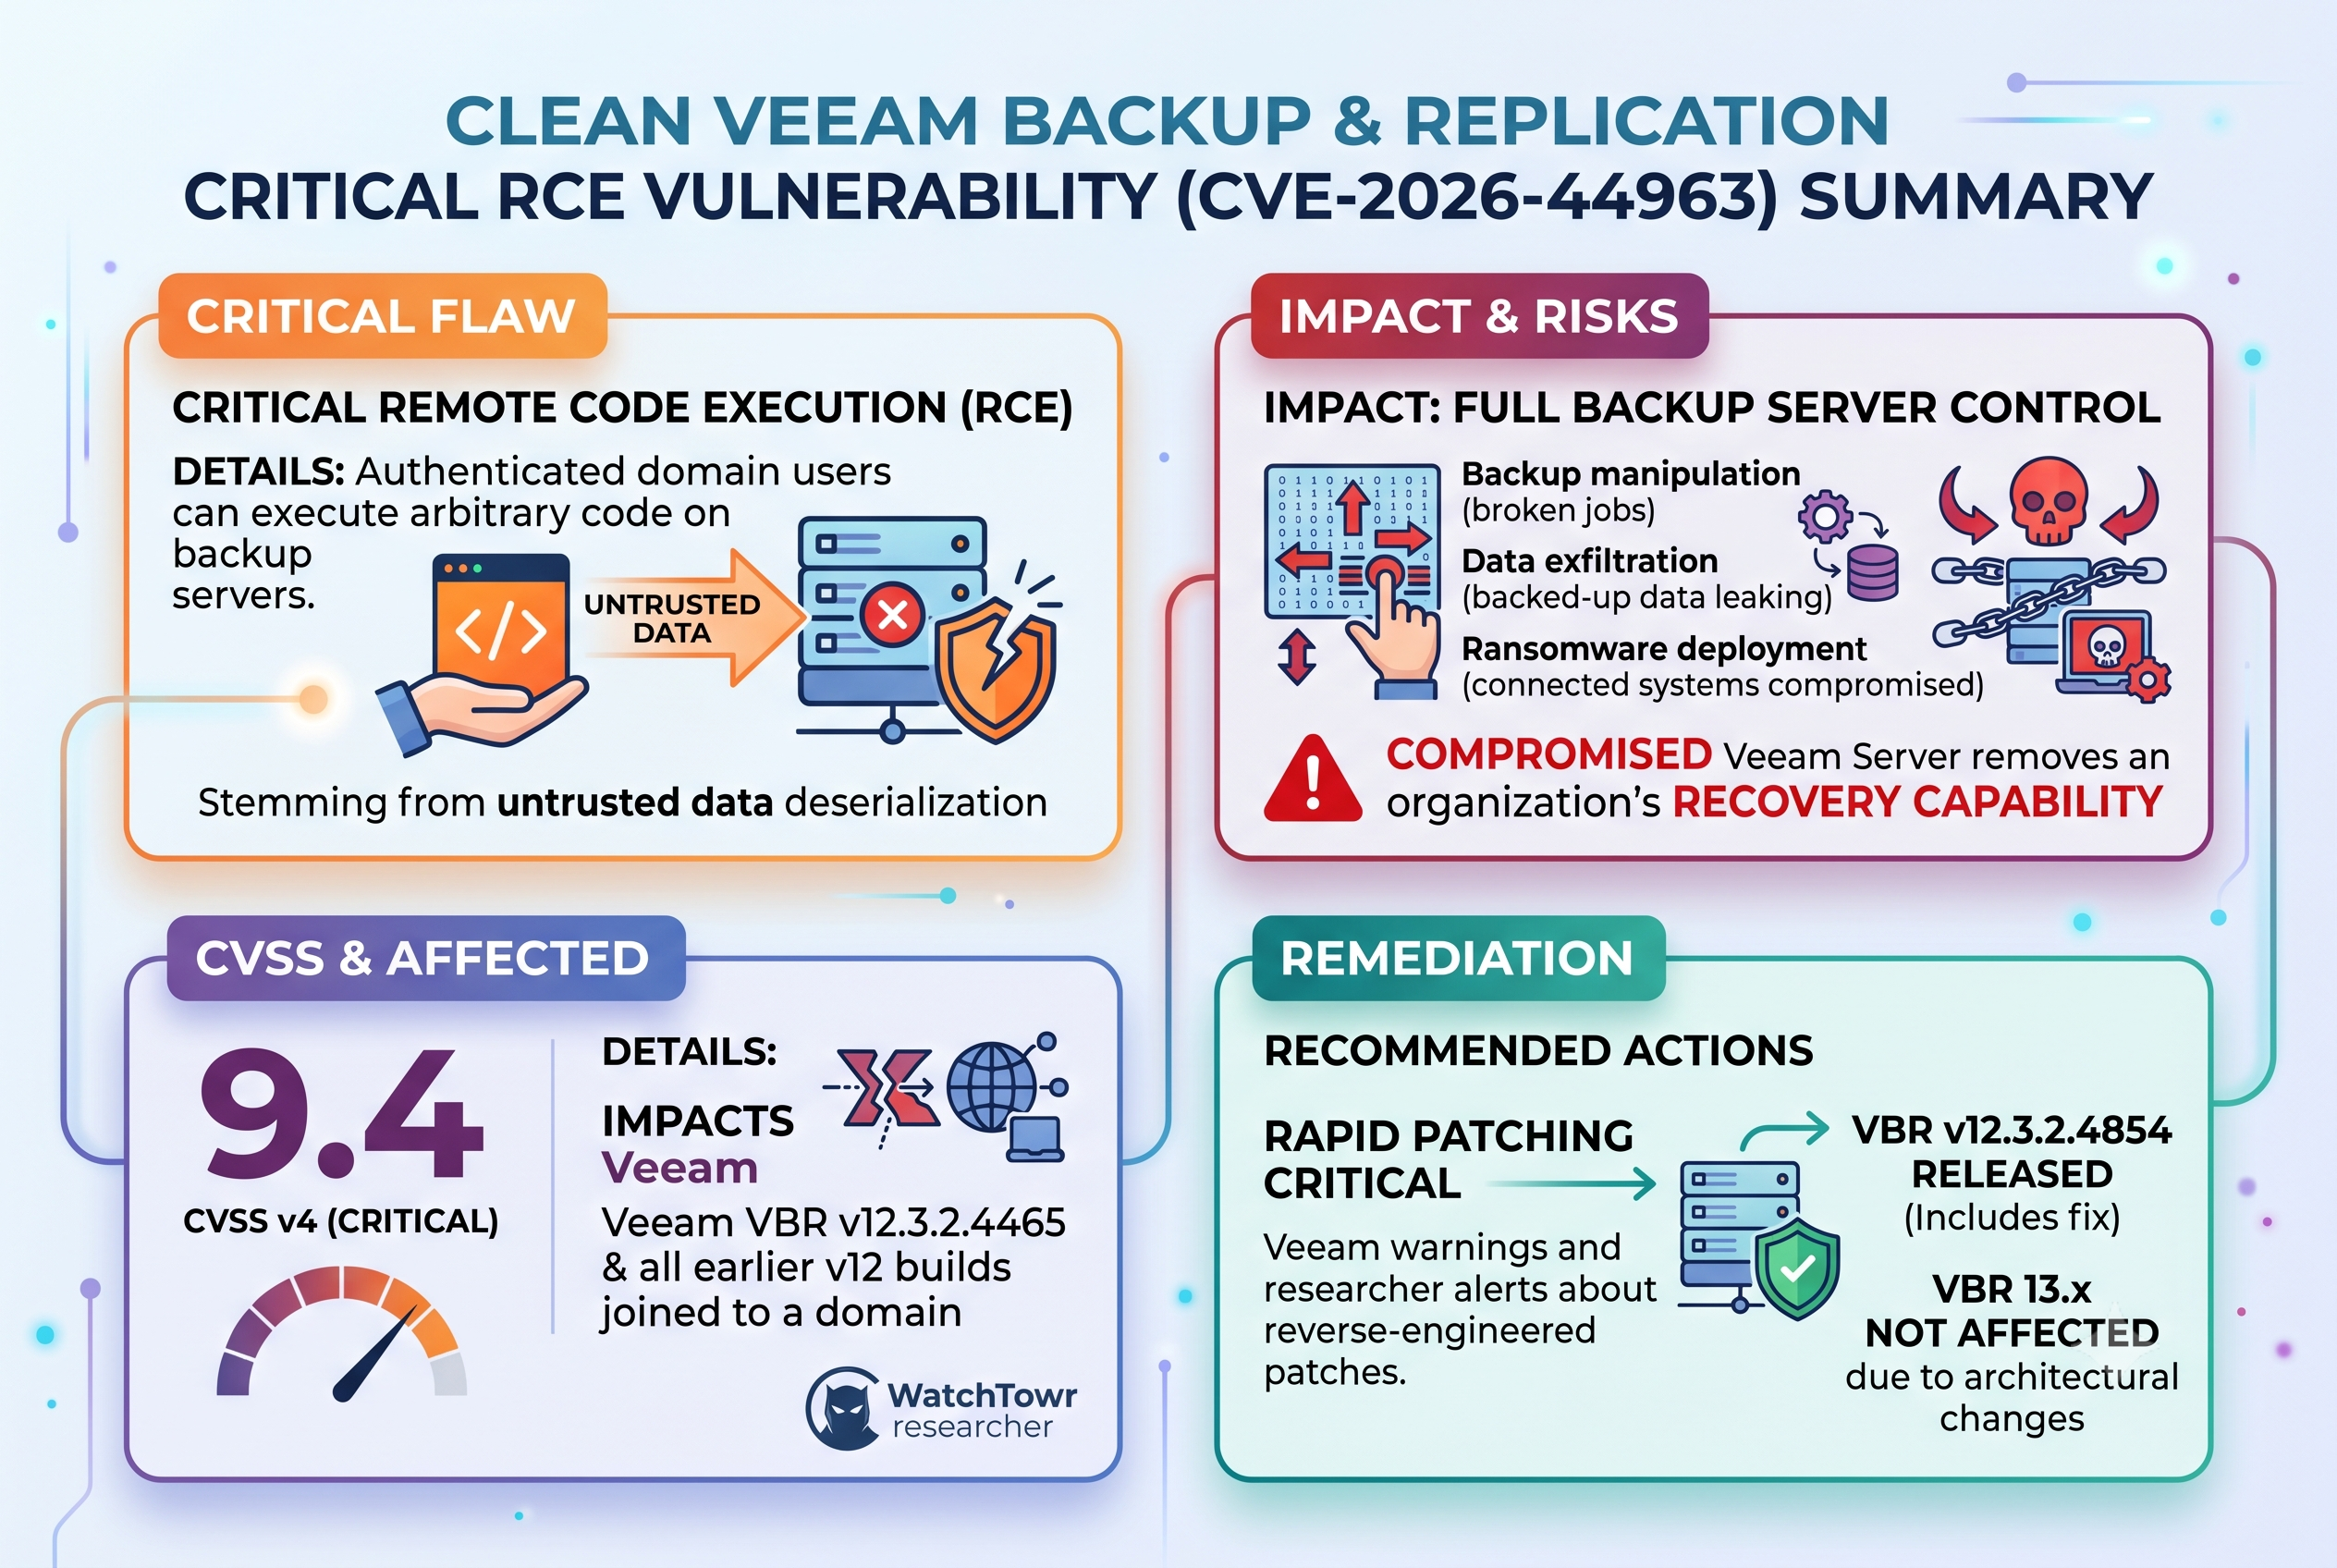
A critical remote code execution vulnerability in Veeam Backup & Replication (VBR), tracked as CVE-2026-44963 (CVSS v4 9.4), allows authenticated domain users to execute arbitrary code on backup servers. The flaw, discovered by WatchTowr researcher Sina Kheirkhah, stems from deserialization of untrusted data and impacts VBR version 12.3.2.4465 and all earlier v12 builds that are joined to a domain.
Successful exploitation grants an attacker full control over the backup server — enabling manipulation of backup jobs, exfiltration of backed-up data, or deployment of ransomware against connected systems. Given that backup infrastructure is routinely the last line of defense against ransomware, a compromised Veeam server effectively removes an organization’s recovery capability.
Veeam has released a fix in version 12.3.2.4854, and VBR 13.x is not affected due to architectural changes. While no active exploitation has been reported yet, Veeam and security researchers warn that attackers routinely reverse-engineer patches to develop exploits for unpatched systems — making rapid patching critical.
Source
The Hacker News — Veeam Backup Replication RCE Flaw · BleepingComputer · Security Affairs
Commentary
Veeam has become a staple of enterprise backup strategy and, by extension, a prime target for ransomware operators. We have seen this pattern repeatedly — Veeam vulnerabilities get weaponized fast because compromising backup infrastructure is the single most effective way to guarantee a ransom payout. CVE-2025-23120 last year followed the same trajectory: patch drops, PoC emerges, exploitation follows within days.
The requirement for domain-joined installations and a low-privileged domain account as prerequisites might sound limiting, but in practice, post-initial-access these conditions are trivially met in most enterprise environments. Organizations running VBR v12 should patch to 12.3.2.4854 immediately. Those still on older branches should accelerate migration plans to v13, which eliminates this vulnerability class entirely through architectural improvements.