

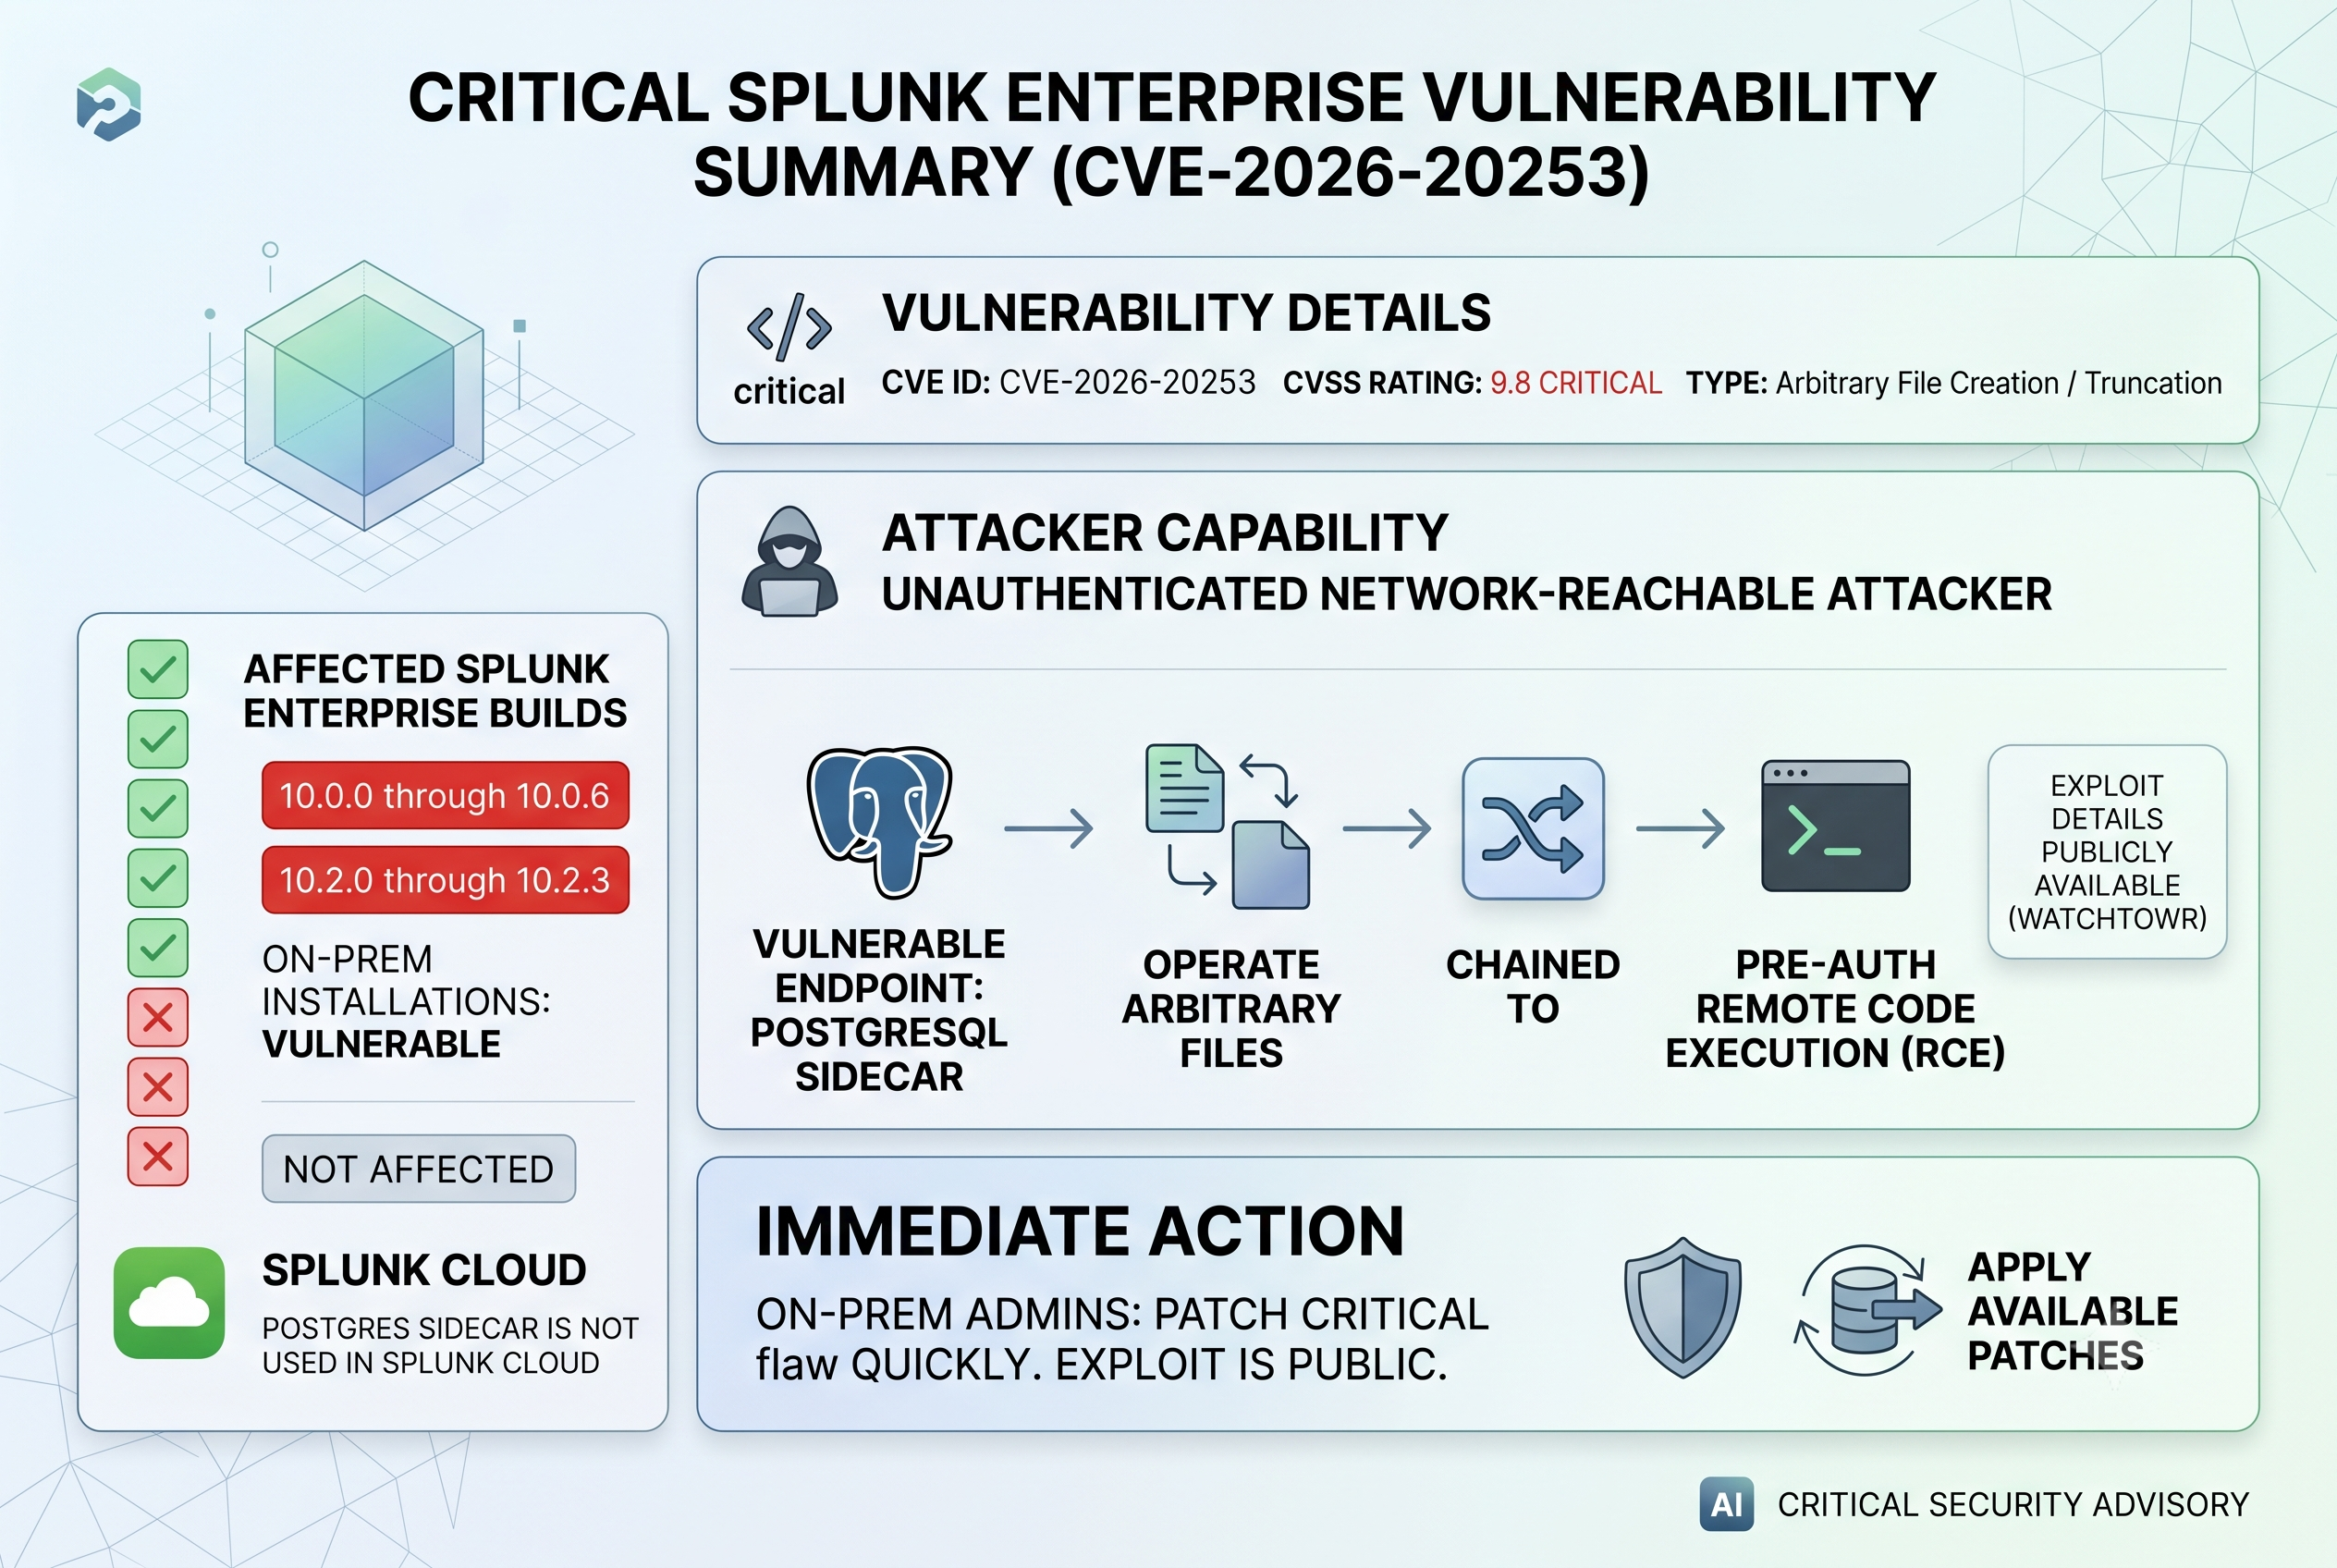
Summary
Splunk has patched a critical flaw in Splunk Enterprise, tracked as CVE-2026-20253, that allows an unauthenticated network-reachable attacker to create or truncate arbitrary files through a PostgreSQL sidecar endpoint. Splunk rates the issue 9.8 CVSS and says affected builds are 10.0.0 through 10.0.6 and 10.2.0 through 10.2.3.
Public technical analysis from watchTowr showed how the file operation primitive can be chained into pre-auth remote code execution by abusing the sidecar backup and restore flow. Splunk says Splunk Cloud is not affected because the vulnerable Postgres sidecar is not used there, but on-prem admins need to move quickly because exploit details are already public.
Source
Splunk advisory SVD-2026-0603
watchTowr technical analysis
Commentary
This is a pure blue-team fire drill: exposed Splunk Enterprise instances are high-value targets, and the gap between public exploit write-up and real-world opportunistic scans is usually short. If your SOC depends on Splunk to see everything else, losing trust in the platform itself is a brutal failure mode.
The practical takeaway is simple. Patch to 10.2.4 or 10.0.7 immediately, verify external exposure, and treat any internet-reachable Splunk Enterprise node as a priority validation target. Defenders should also review file integrity and process execution around Splunk app directories for signs of post-exploitation.