

Summary
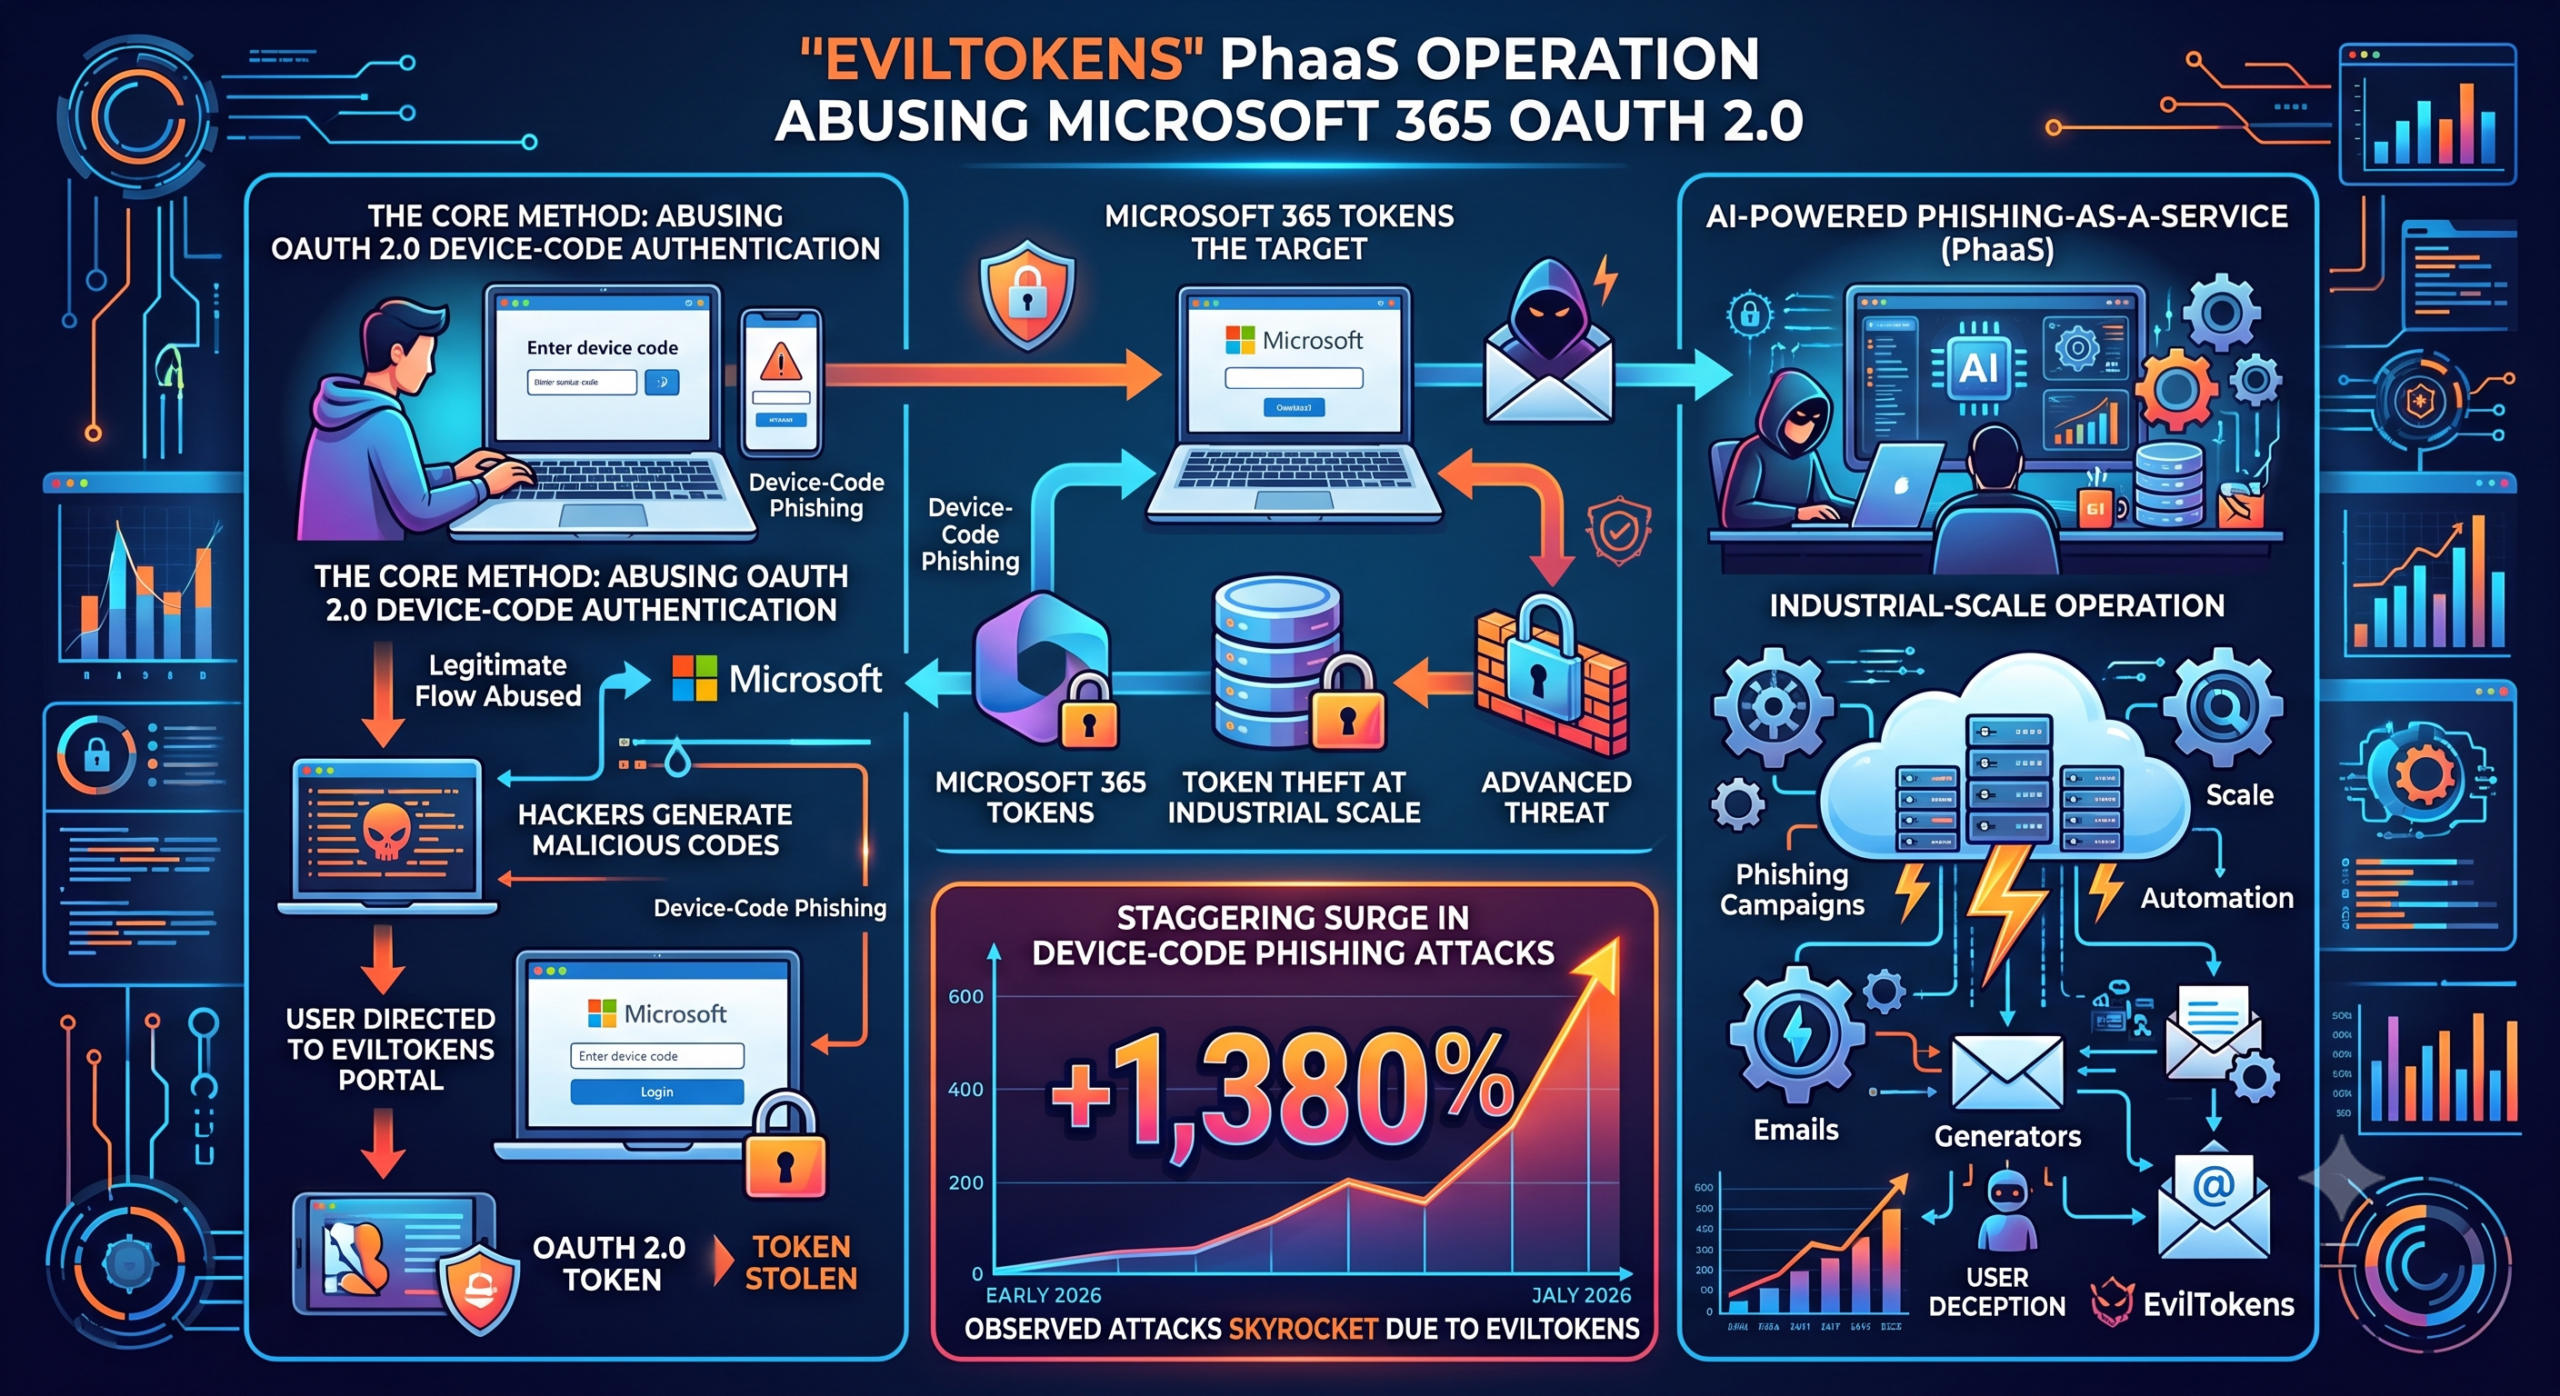
Researchers have detailed “EvilTokens,” a sophisticated AI-powered phishing-as-a-service (PhaaS) operation that abuses Microsoft’s legitimate OAuth 2.0 device-code authentication flow to steal Microsoft 365 tokens at industrial scale. The operation has contributed to a staggering 1,380% surge in device-code phishing attacks observed in early 2026.
Device-code phishing exploits a legitimate authentication mechanism designed for devices with limited input capabilities (smart TVs, IoT devices). Attackers generate a device code and trick victims into entering it on Microsoft’s real login page, which then grants the attacker a valid OAuth token — completely bypassing MFA. EvilTokens automates this entire pipeline with AI-generated lures, automated code generation, and real-time token harvesting, lowering the barrier to entry for even unsophisticated threat actors.
The operation is particularly dangerous for blue teams because the authentication occurs through Microsoft’s legitimate infrastructure — there’s no phishing page to block, no suspicious domain to flag, and the resulting tokens are indistinguishable from legitimate ones. Traditional email security and URL filtering provide zero protection against this attack vector.
Sources
Commentary
Device-code phishing is arguably the most elegant identity attack in the current threat landscape, and EvilTokens has turned it into a turnkey service. The reason it’s so effective is that defenders’ traditional controls are completely blind to it — the victim authenticates on the real Microsoft login page, the token is legitimate, and MFA is satisfied. There’s nothing to detect at the network or email layer.
Blue teams need to focus on conditional access policies that restrict or disable the device-code authentication flow entirely, monitor for anomalous device-code grant activity in Azure AD sign-in logs, and implement token binding where possible. If your organization doesn’t use smart TVs or IoT devices that require device-code auth, disable it. The 1,380% surge tells you everything you need to know about where attackers are heading.