

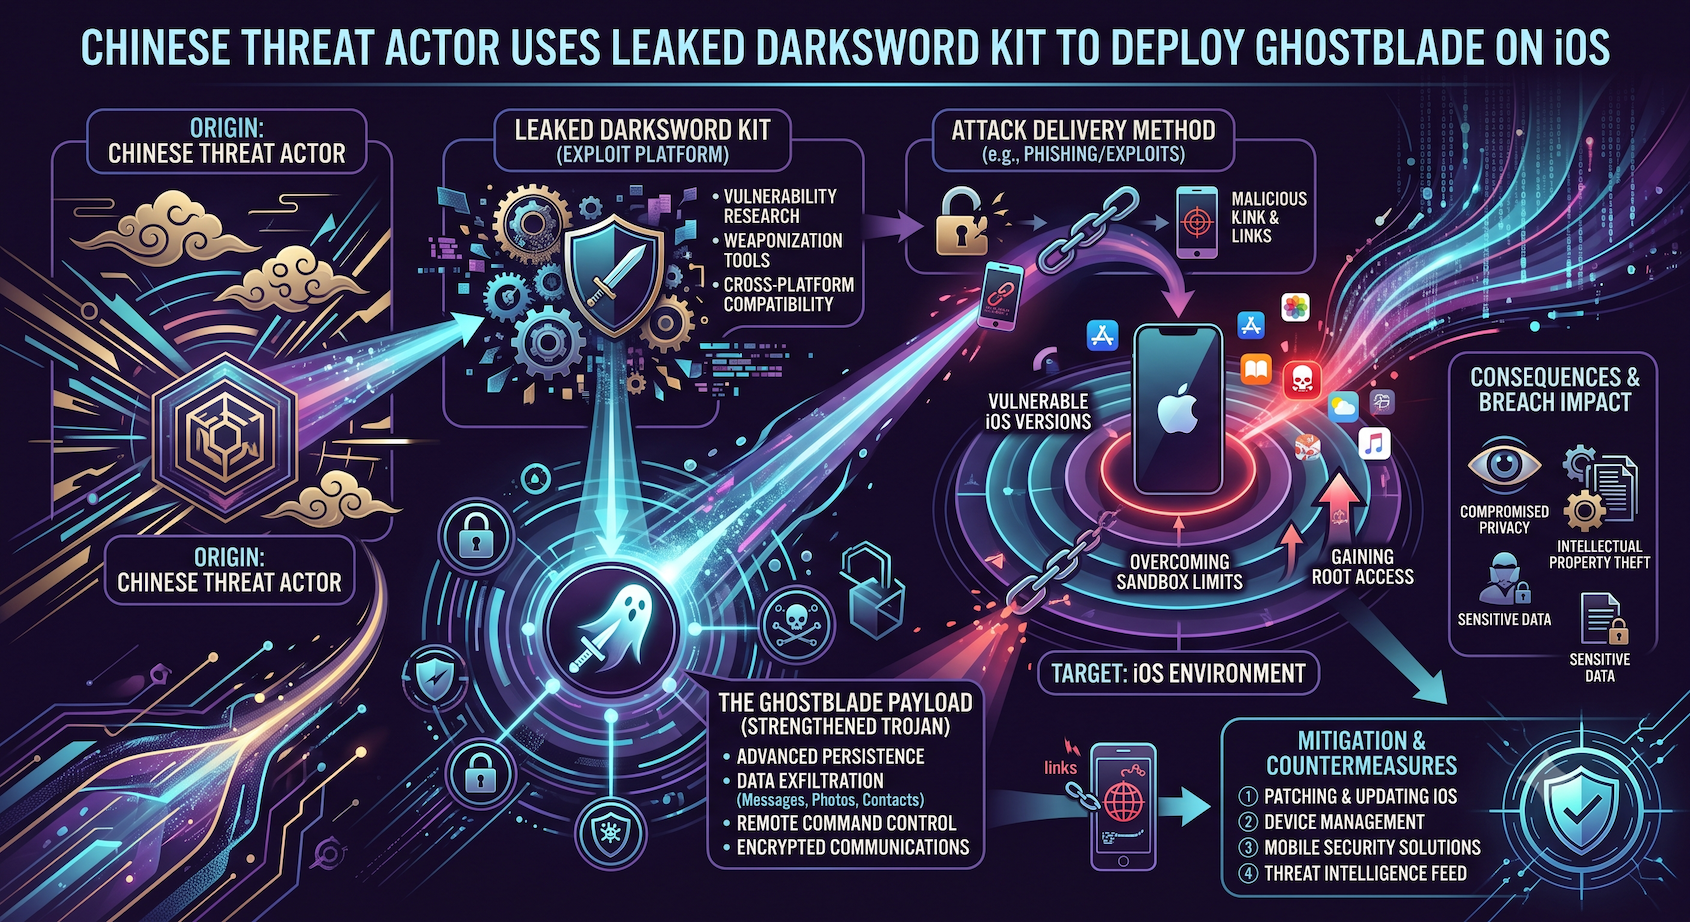
An unknown Chinese-speaking threat actor has been running a campaign targeting Apple iOS devices by leveraging a publicly leaked version of the DarkSword exploit kit. Attack surface management platform Censys identified the threat actor operating more than 100 web properties, most of which are fake Amazon Web Services (AWS) sign-in pages hosted on domains that also serve the exploit payload.
The campaign deploys GHOSTBLADE, a previously undocumented iOS malware, through social engineering tactics that trick users into visiting malicious AWS login pages. The use of a leaked exploit kit suggests the threat actor is opportunistic, adapting known tools for their own campaigns rather than developing custom exploits from scratch.
Why This Matters: The proliferation of leaked exploit kits in the hands of threat actors lowers the barrier to entry for sophisticated attacks. This campaign demonstrates how publicly available tools can be weaponized at scale — with over 100 fake infrastructure points already deployed. iOS users should be vigilant about unexpected AWS login prompts and verify URLs before entering credentials. Security teams should monitor for GHOSTBLADE indicators of compromise and review Censys’ full analysis.
Sources:
The Hacker News — Full Article
Censys Analysis