

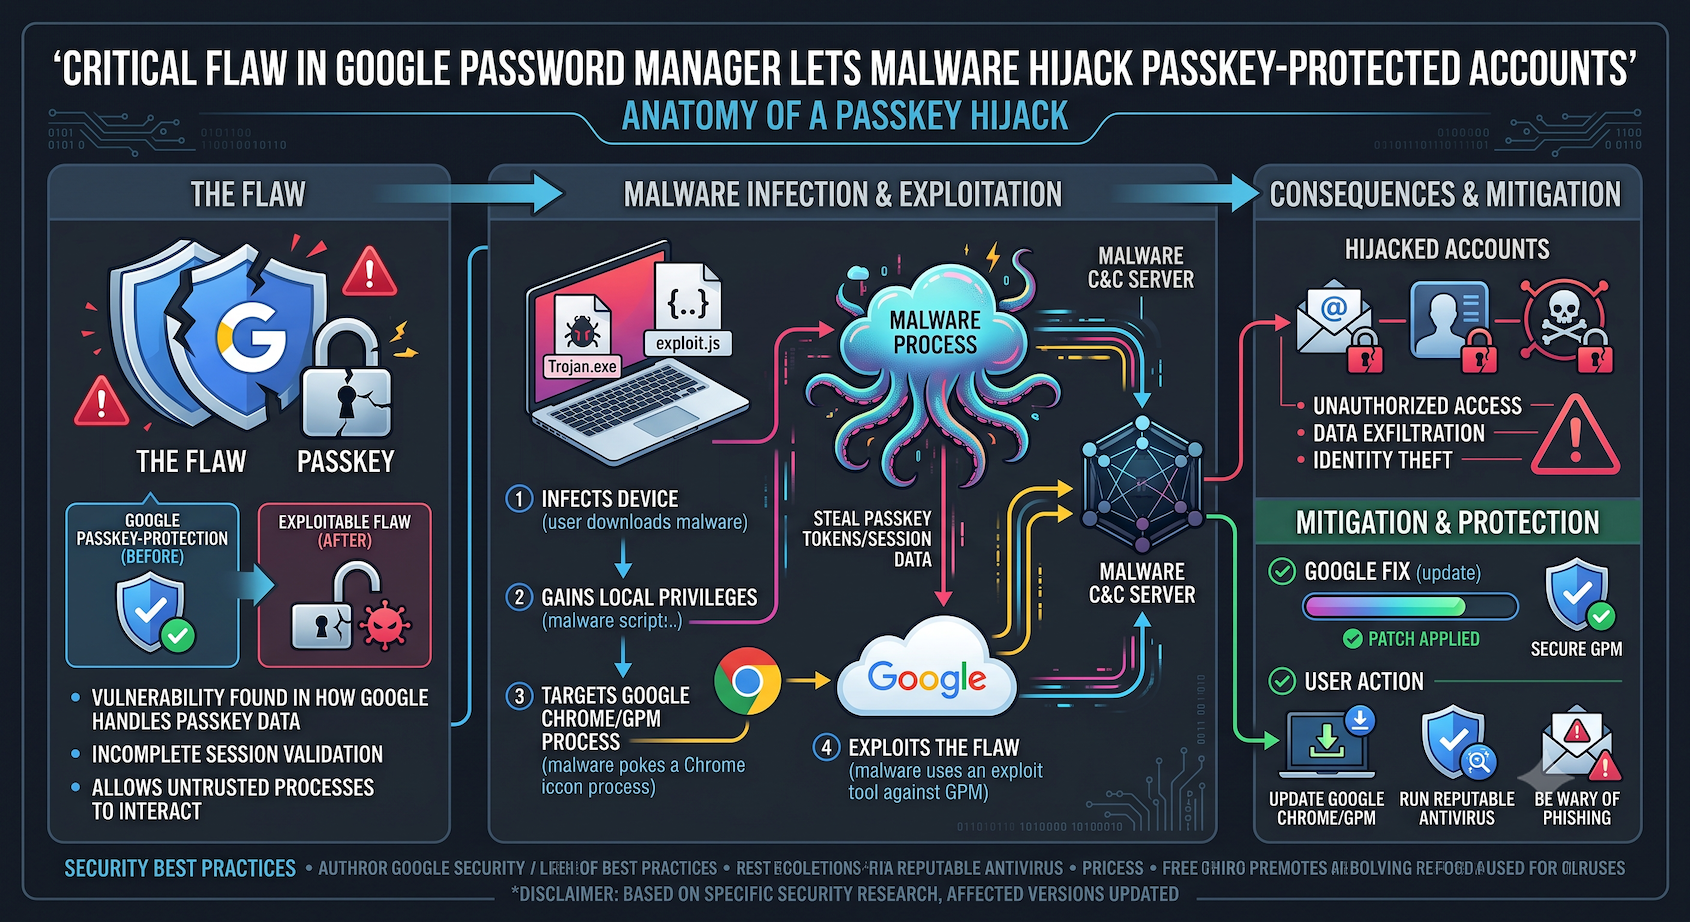
Unit 42 has disclosed three attack paths against Chrome’s Google Password Manager cloud authenticator, dubbed Pass-ta-key, Silver Pass-ta-key, and Golden Pass-ta-key. The strongest variant targets the master key, enabling malware running as an ordinary user on a Windows machine to sign into passkey-protected accounts without requiring a fingerprint, PIN, or any visible interaction from the victim.
This is significant because passkeys were designed to be phishing-resistant and eliminate the need for passwords entirely. If an attacker can bypass biometric verification at the OS level through the cloud authenticator, the entire passkey trust model is undermined for millions of users. The attack requires no user interaction and leaves no visible traces on screen.
Why This Matters: Google’s own password manager is being used to bypass the very security mechanism it was designed to provide. Users relying on passkeys for banking, email, and cloud services may have a false sense of security. Organizations should audit their passkey deployment and consider supplementary MFA controls until patches are widely deployed.
Sources:
The Hacker News — Full Article
Unit 42 Technical Analysis