

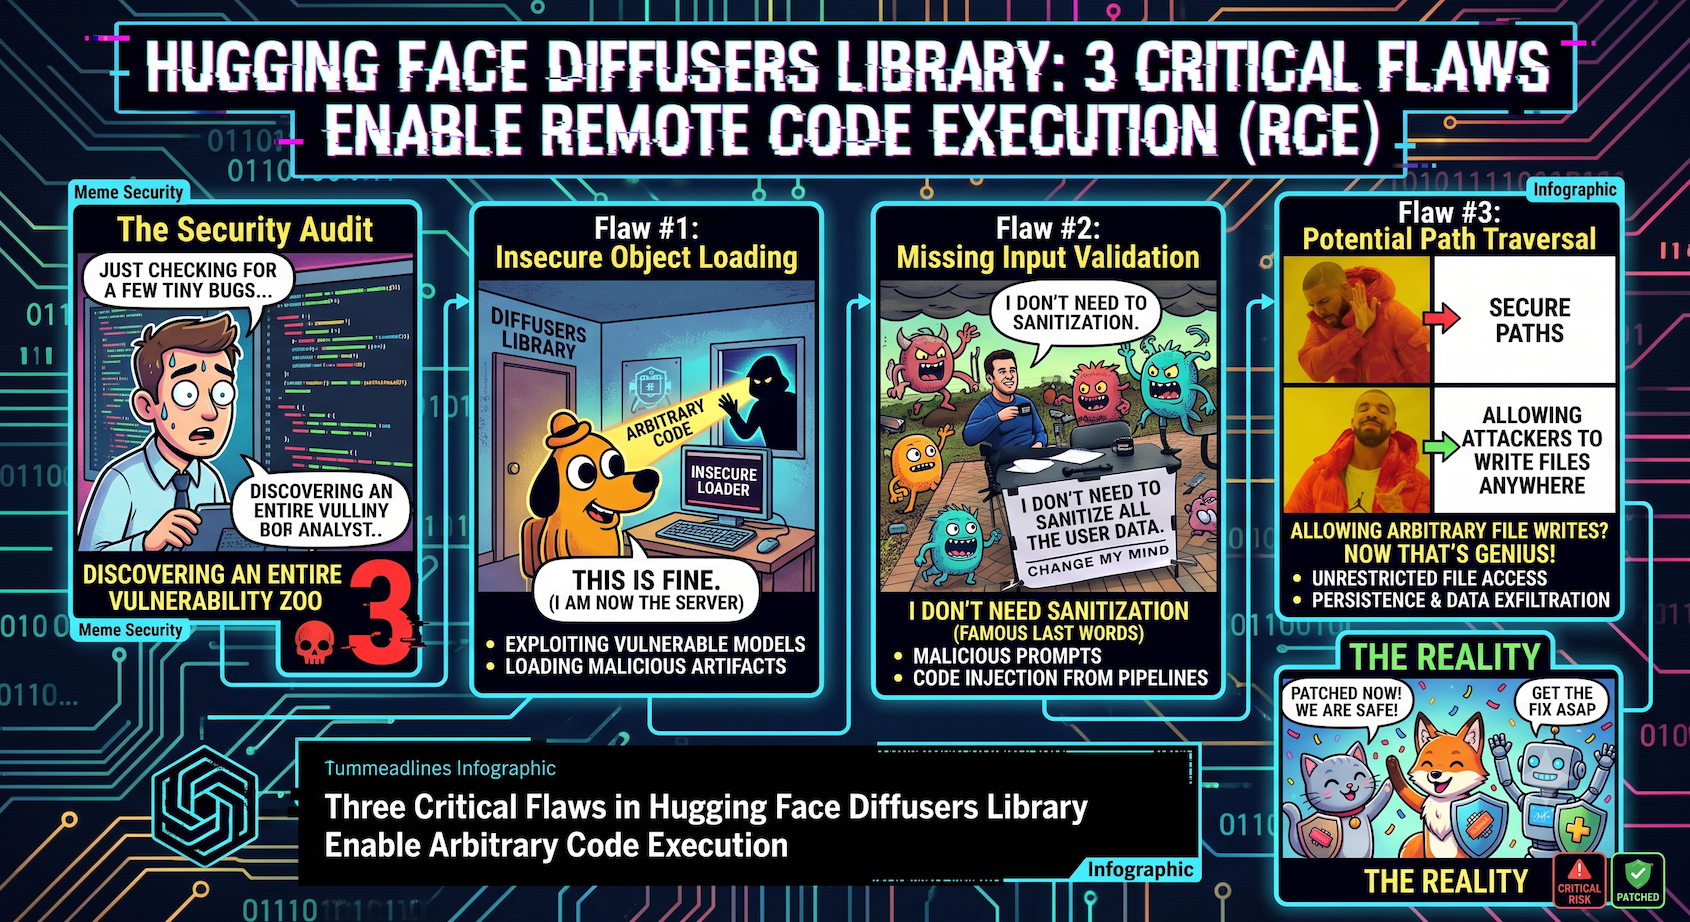
Three high-severity security vulnerabilities have been disclosed in Hugging Face’s Diffusers library that could allow crafted model repositories to stealthily execute arbitrary code on machines that load them. Critically, these vulnerabilities bypass trust_remote_code, the safeguard designed to prevent unreviewed code from running in the Diffusers ecosystem.
This represents a significant AI supply chain risk. The Diffusers library is one of the most widely used frameworks for loading and running machine learning models, particularly in generative AI applications. If attackers can poison model repositories with malicious code that executes during the loading process, every organization using compromised models could be affected — regardless of their security posture.
Why This Matters: The AI supply chain is increasingly under attack. These vulnerabilities demonstrate that even trusted platforms like Hugging Face are not immune to supply chain compromises. Organizations using Diffusers should immediately audit their model repositories, ensure they’re running patched versions, and implement strict controls on which models are loaded in production environments. The bypass of trust_remote_code is particularly alarming as it defeats a key security control.
Sources:
The Hacker News — Full Article