

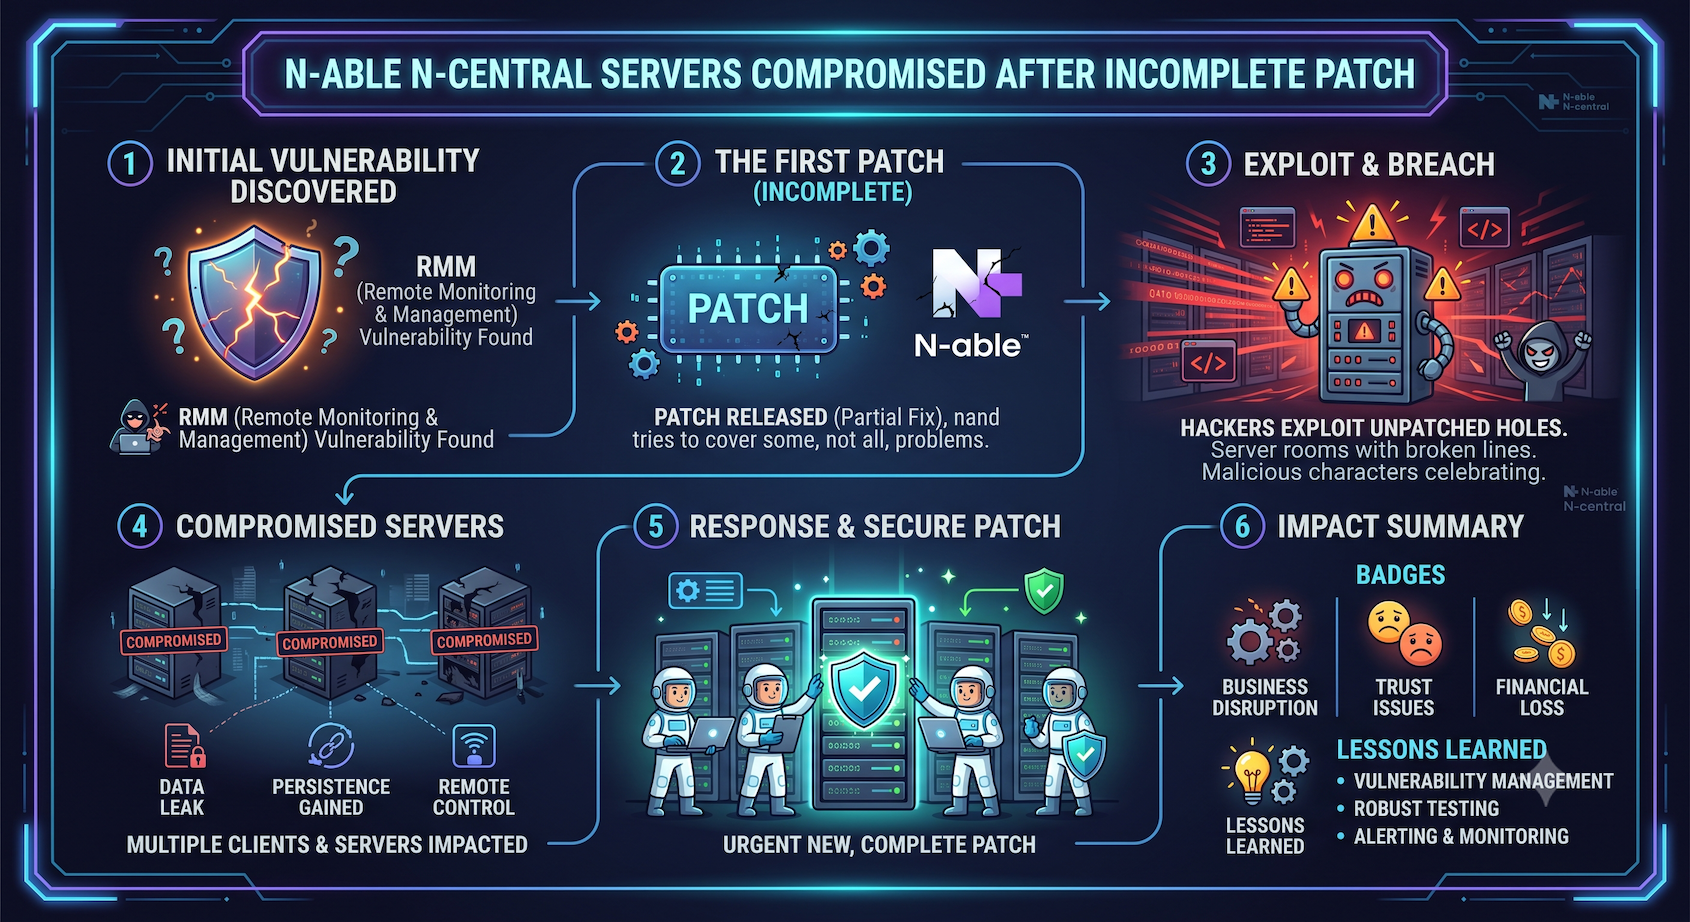
N-able has confirmed that attackers are exploiting an authentication bypass in N-central (CVE-2026-18577) to gain remote administrative access and reach customer systems managed through those servers. The critical detail: N-able’s first fix was incomplete, allowing attackers to continue compromising environments even after the initial patch was applied.
CVE-2026-18577 affects N-central builds prior to 2026.3.1.7, which was shipped on August 2 as the first unaffected version. N-central is a widely deployed remote monitoring and management (RMM) platform, making this vulnerability particularly dangerous as compromise of a single server can lead to lateral movement across entire customer networks.
Why This Matters: Incomplete patches are among the most dangerous scenarios in vulnerability management. Organizations that applied N-able’s initial fix may still be compromised. This incident highlights the importance of verifying patch effectiveness and monitoring for indicators of compromise even after remediation steps are applied. N-central users should immediately verify they’re running build 2026.3.1.7 or later and audit their environments for signs of compromise.
Sources:
The Hacker News — Full Article