

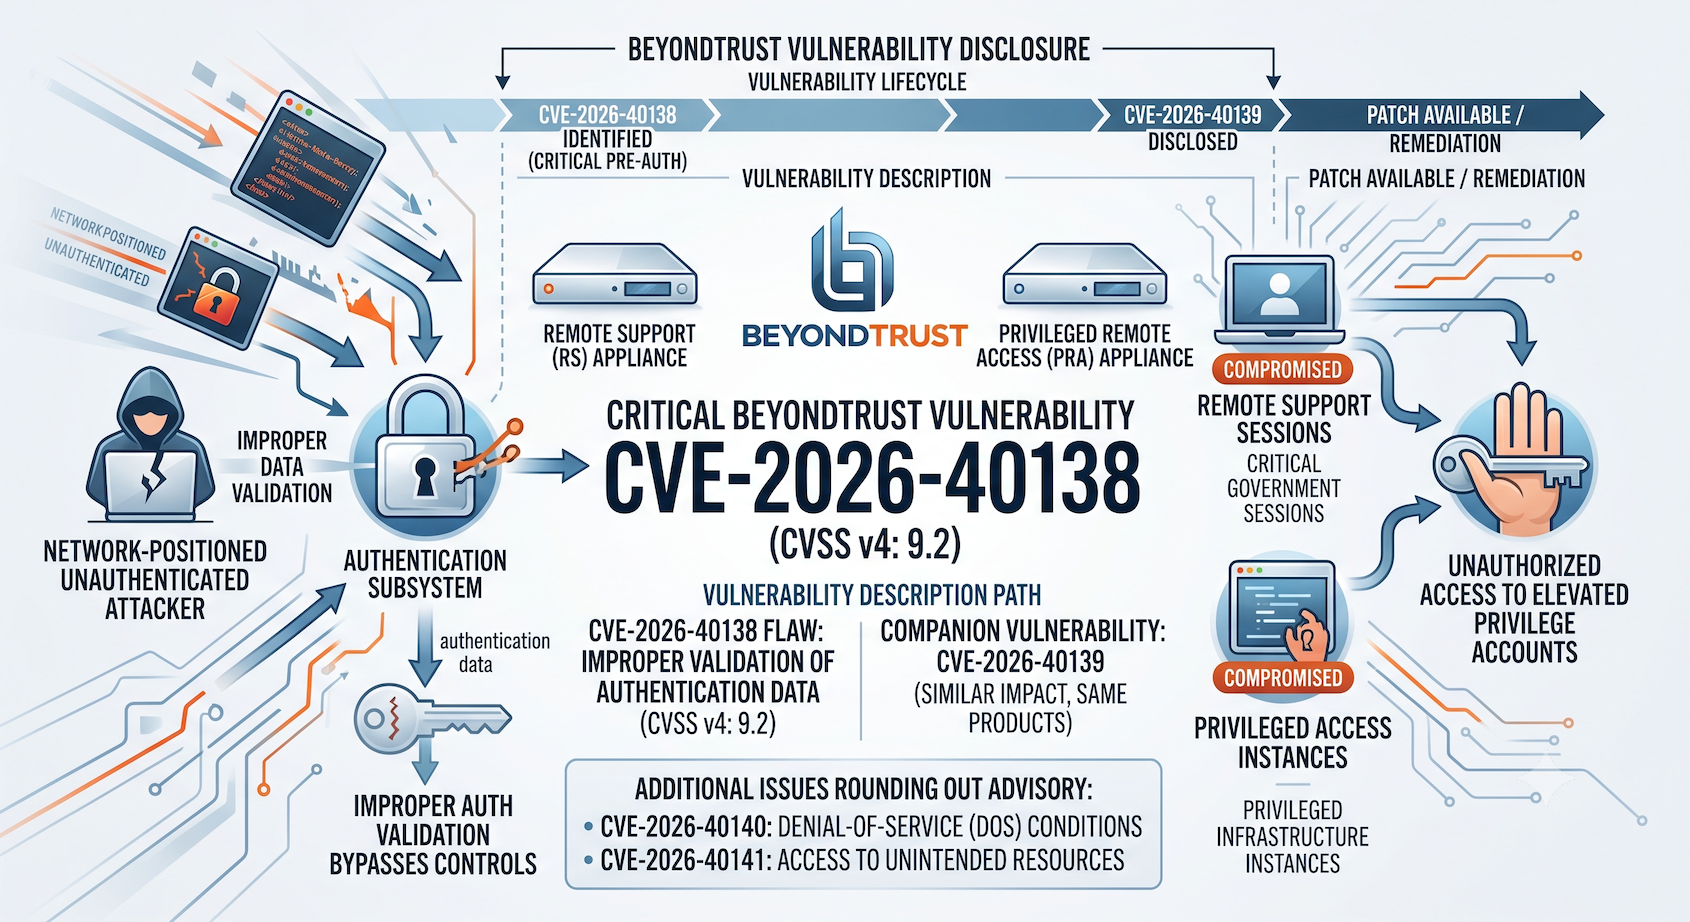
BeyondTrust has disclosed a critical pre-authentication vulnerability — CVE-2026-40138 (CVSS v4: 9.2) — affecting its Remote Support (RS) and Privileged Remote Access (PRA) appliances. The flaw stems from improper validation of authentication data within the authentication subsystem, allowing a network-positioned unauthenticated attacker to bypass access controls and gain unauthorized access to accounts with elevated privileges. A companion vulnerability, CVE-2026-40139, is also patched in the same update, affecting the same products with similar impact. Two additional issues — CVE-2026-40140 and CVE-2026-40141 — round out the advisory, covering denial-of-service conditions and access to unintended resources.
Affected versions are Remote Support and Privileged Remote Access 25.3.2 and earlier. BeyondTrust proactively identified the vulnerabilities and released fixes ahead of any observed exploitation. Cloud-hosted instances were automatically patched on April 21, 2026. Self-hosted customers must apply the April 2026 Security Rollup or upgrade to version 25.3.3 or later immediately. BeyondTrust notes that successful exploitation of CVE-2026-40138 requires a specific authentication configuration to be enabled, the details of which have not been publicly disclosed to reduce weaponization risk.
BeyondTrust products sit at the heart of privileged access management architectures in large enterprises and government agencies. The company suffered a high-profile compromise in December 2024 when attackers exploited a different API command injection flaw to access the U.S. Treasury Department’s systems — a history that makes the speed of patching these new flaws especially important.
Sources
- BleepingComputer — BeyondTrust Warns of Critical Flaws in Remote Access Software
- The Hacker News — BeyondTrust Patches Critical Auth Bypass
- BeyondTrust — Security Advisory BT26-03
Commentary
Pre-authentication bypasses in internet-facing privileged access management appliances are among the most sought-after vulnerabilities in enterprise environments — they offer a direct, credential-free path into systems that were specifically designed to protect the most sensitive access in an organization. The fact that BeyondTrust found and patched this proactively, before observed exploitation, is a positive sign, but the window between a patch release and active weaponization is measured in days, not weeks, for this class of product. If you’re running RS or PRA and haven’t applied the April 2026 Security Rollup, stop reading this and go patch.
Blue teams should also review authentication logs for unusual session activity going back to late April 2026 — the date cloud instances were patched provides a rough upper bound for the exposure window on self-hosted deployments that haven’t yet updated. Any privileged sessions that can’t be correlated to a known administrator action warrant investigation. Given BeyondTrust’s previous breach history with state-level threat actors, assume motivated adversaries are aware of this advisory.