

Summary
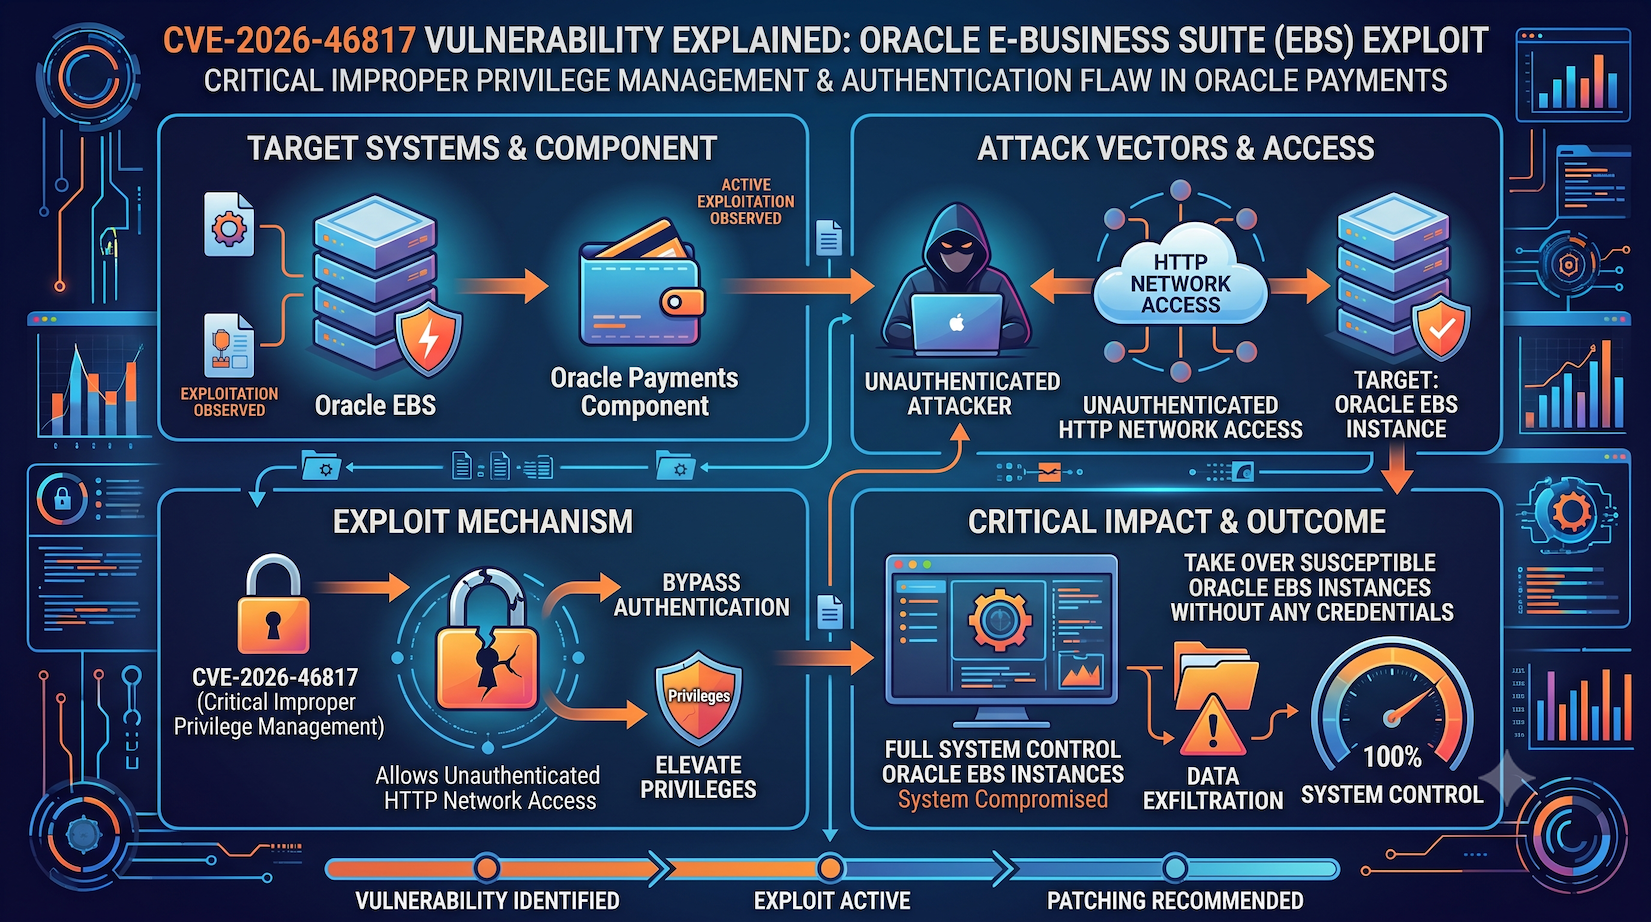
Attackers are actively exploiting CVE-2026-46817, a critical improper privilege management and authentication flaw in Oracle E-Business Suite’s Oracle Payments component. The vulnerability allows unauthenticated attackers with HTTP network access to take over susceptible Oracle EBS instances without any credentials.
The flaw was disclosed as part of Oracle’s recent Critical Patch Update, but exploitation in the wild was confirmed in late June 2026 by multiple threat intelligence sources. Given that Oracle E-Business Suite is widely deployed across large enterprises for financial operations, procurement, and supply chain management, the impact is potentially enormous — successful exploitation gives attackers access to financial transaction data, payment records, and core business workflows.
This follows on the heels of the ShinyHunters campaign that exploited Oracle PeopleSoft across 100+ organizations earlier in June, suggesting Oracle’s enterprise product line is under sustained and coordinated attack from multiple threat actors.
Sources
- The Hacker News — Oracle E-Business Suite Flaw CVE-2026-46817
- Security Boulevard — Hackers Now Exploit Critical Oracle EBS Flaw
Commentary
Oracle’s enterprise suite is having a brutal June. Between PeopleSoft getting mass-exploited by ShinyHunters and now E-Business Suite’s Payments component getting popped unauthenticated, organizations running Oracle should be in full triage mode. The common thread is pre-auth takeover — attackers don’t need stolen credentials, they just need network access to the application.
If your Oracle EBS instances are internet-facing (and too many are), this is a stop-everything-and-patch situation. The Payments component specifically handles financial transactions, which means exploitation could lead to financial fraud, data exfiltration, and serious regulatory exposure.